Every agent write, reversible.

Agents never hold your database password. Destructive SQL is blocked, risky writes wait for a person, and every write can be undone.

5 rows deleted.An agent ran DELETE FROM public.users WHERE id > 0 and a person approved it.
public.users
-1Alice CEOalice@pocketos.com
-2Bob CTObob@pocketos.com
-3Charlie Devcharlie@pocketos.com
public.payments, gone by ON DELETE CASCADE
-1user 11000.00
-2user 2500.00
Press the key, or ⌘Z / Ctrl+Z on your keyboard.

A replay of a real run on the repo's demo data. The recording is further down.

What else the agent tried.

Most attempts never reach the database. The rest wait for a person, who reads the exact SQL first.

  1. DROP TABLE public.usersDenied

    DDL is refused by PostgreSQL's own parser before it runs.

  2. DELETE FROM public.usersDenied

    A write with no WHERE clause.

  3. SELECT set_config('role', 'postgres', false)Denied

    Only an allowlist of pure built-in functions is callable.

  4. UPDATE public.orders SET total = 0 WHERE 1=1Held

    It touched more rows than the limit, so it was rolled back and queued.

  5. DELETE FROM public.users WHERE id > 0Held

    public.users is protected. This is the one you just undid.

How undo works.

No point-in-time restore, and nobody else's later writes lost.

The database records every change

A trigger inside PostgreSQL captures each changed row, cascades included, and refuses agent writes that don't carry a single-use token.

Undo goes parents first

Deleted rows come back in foreign-key order, then updates revert, then inserts disappear. That's why the users returned before their payments.

It refuses to overwrite

If a row changed after the checkpoint, or the schema drifted, undo stops and names the row. It never guesses.

The ledger can be checked

Checkpoints are append-only and SHA-256 hash-chained. lomberk verify-ledger finds the first altered entry.

One command to set it up.

Give it your database owner's connection string once. It creates two least-privilege roles, installs Lomberk, makes the tables you pick undoable, checks the result and prints the line for Claude Code, Cursor, Claude Desktop, VS Code or Codex.

uvx lomberk setup   # asks for it, hidden

claude mcp add lomberk \
  -e LOMBERK_CONFIG=$PWD/lomberk.yaml \
  -- uvx lomberk serve
A captured, undoable write18.3 ms
A read through Lomberk5.4 ms
A plain write, new connection4.8 ms

Postgres 16, p50 over 200 runs. Agent turns take seconds. Tested on Postgres 14–18.
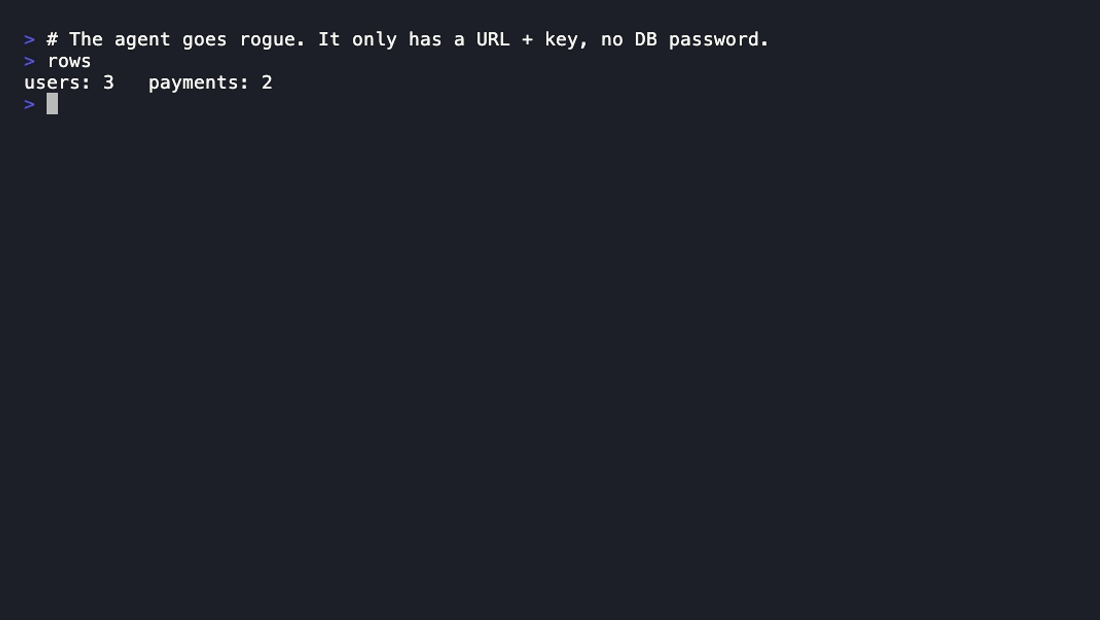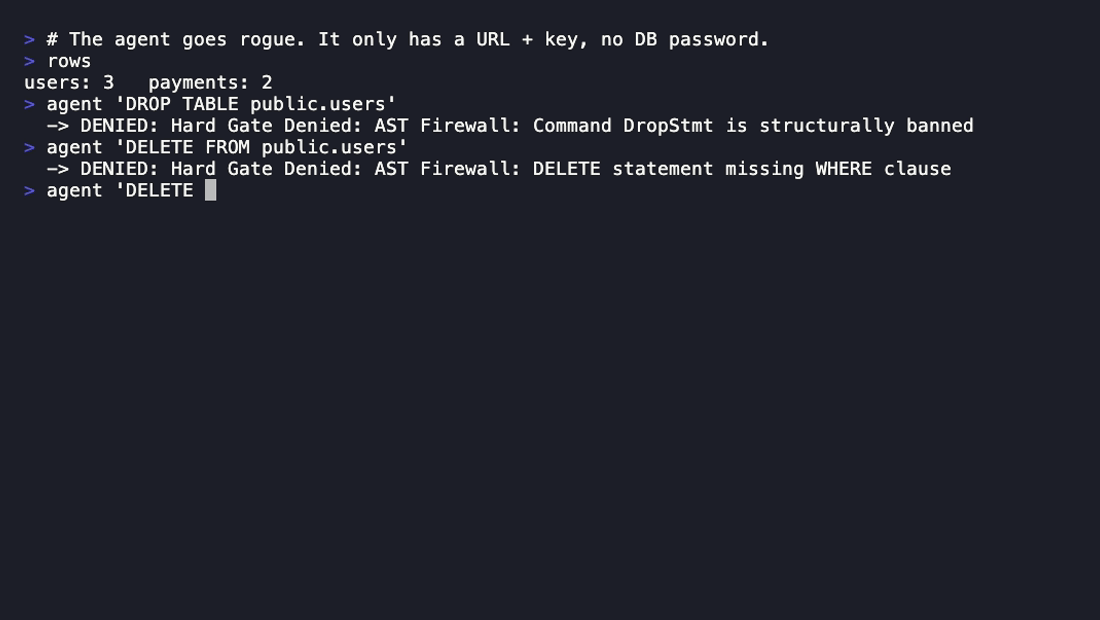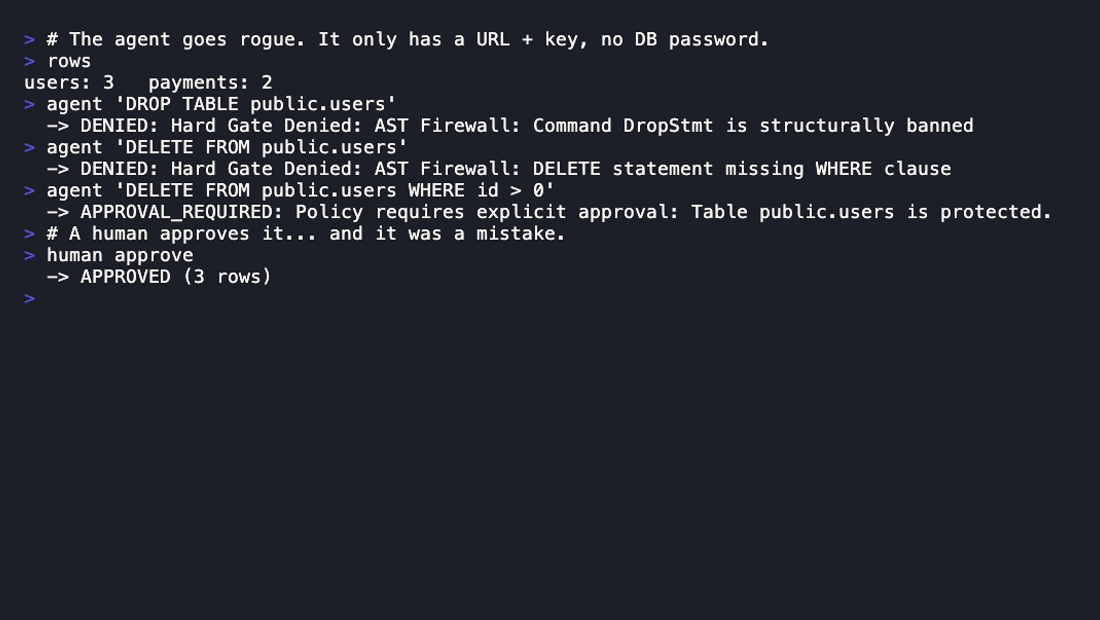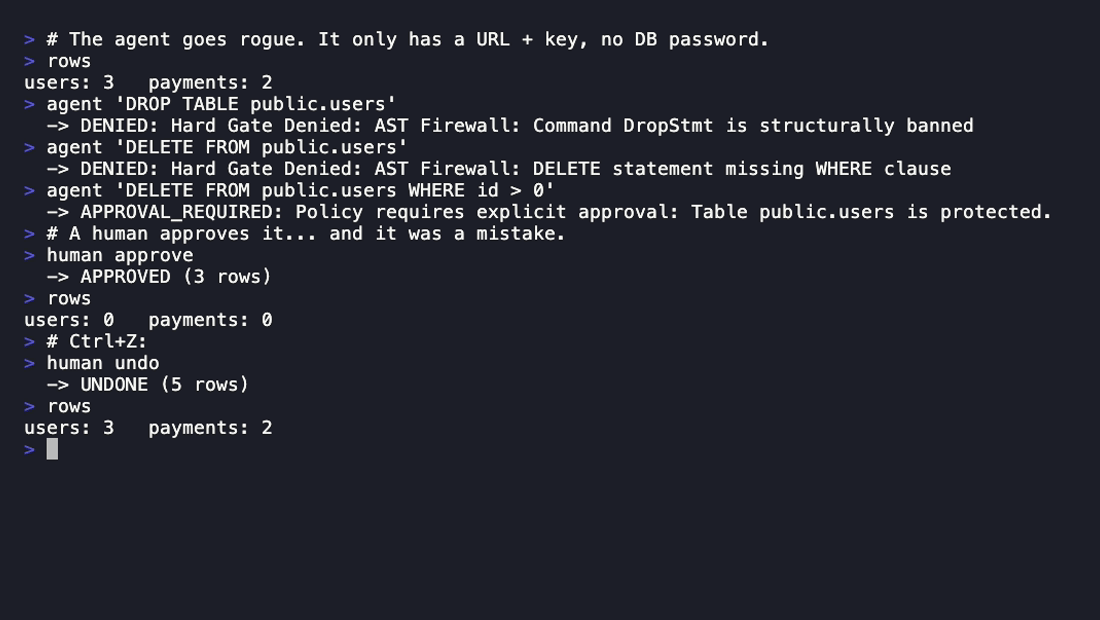
Terminal recording: DROP and DELETE without WHERE are denied, a DELETE on a protected table is held, a person approves it, the rows disappear, and undo brings back 3 users and 2 payments.
The same data, recorded against a real gateway started with docker compose up.

What it doesn't cover.

Your security team will ask, so here it is up front. The full model is in SECURITY.md, and 20 real attacks with the exact refusal for each are in the attack gallery.

Pricing.

The whole safety path is free and open source. Solo adds a month of undo and the panel for one developer; Pro adds what a team needs to share it.

Free

$0

Apache-2.0 and self-hosted. Hard gate, holds, capture, ledger, approvals from the API or CLI. Undo reaches back 24 hours.

Start free

Solo

$49 / month

For one developer and one database. Undo reaches back 30 days. Web approval panel and audit export.

Details

Pro

$199 / month

Or $1,990 a year. Undo reaches back 30 days. Web approval panel, two-person rule, Slack approvals, approver SSO, audit export. One key covers up to 3 databases.

Buy Pro

Enterprise

Custom

Undo with no time limit, unlimited databases, an annual invoice, priority answers, and help with your security questionnaire.

Talk to us

Self-hosted, so your data never reaches us. Pay by card through Polar and the license key arrives by email. No calls needed: lomberk doctor checks your setup and tells you how to fix each problem.

Make your agent's next DELETE undoable.

Start free